Audit, risk and compliance, with the board at the core.
GovernCore keeps the risk register, the control library, compliance obligations and internal audit on one record, and brings it to the board in its packs, minutes and resolutions. Every paper the board reads is backed by the evidence behind it, and every decision is followed through.
The principles GovernCore is built on, minuted the way your board would.
1.
That every paper the board reads is backed by the register it came from, frozen as it stood on the day the pack went out.
2.
That a control is described once and tested once, and that risk, compliance and audit all read the same result.
3.
That every finding, risk treatment, compliance gap and board decision becomes an action, with an owner, a date, and someone other than the owner to confirm it is done.
4.
That nothing is approved, adopted or signed except by a named person, and that the record shows who, and when.
Carried.
What it does
Five parts, one record. Open any of them.
Risk and controls
A register the committee can read
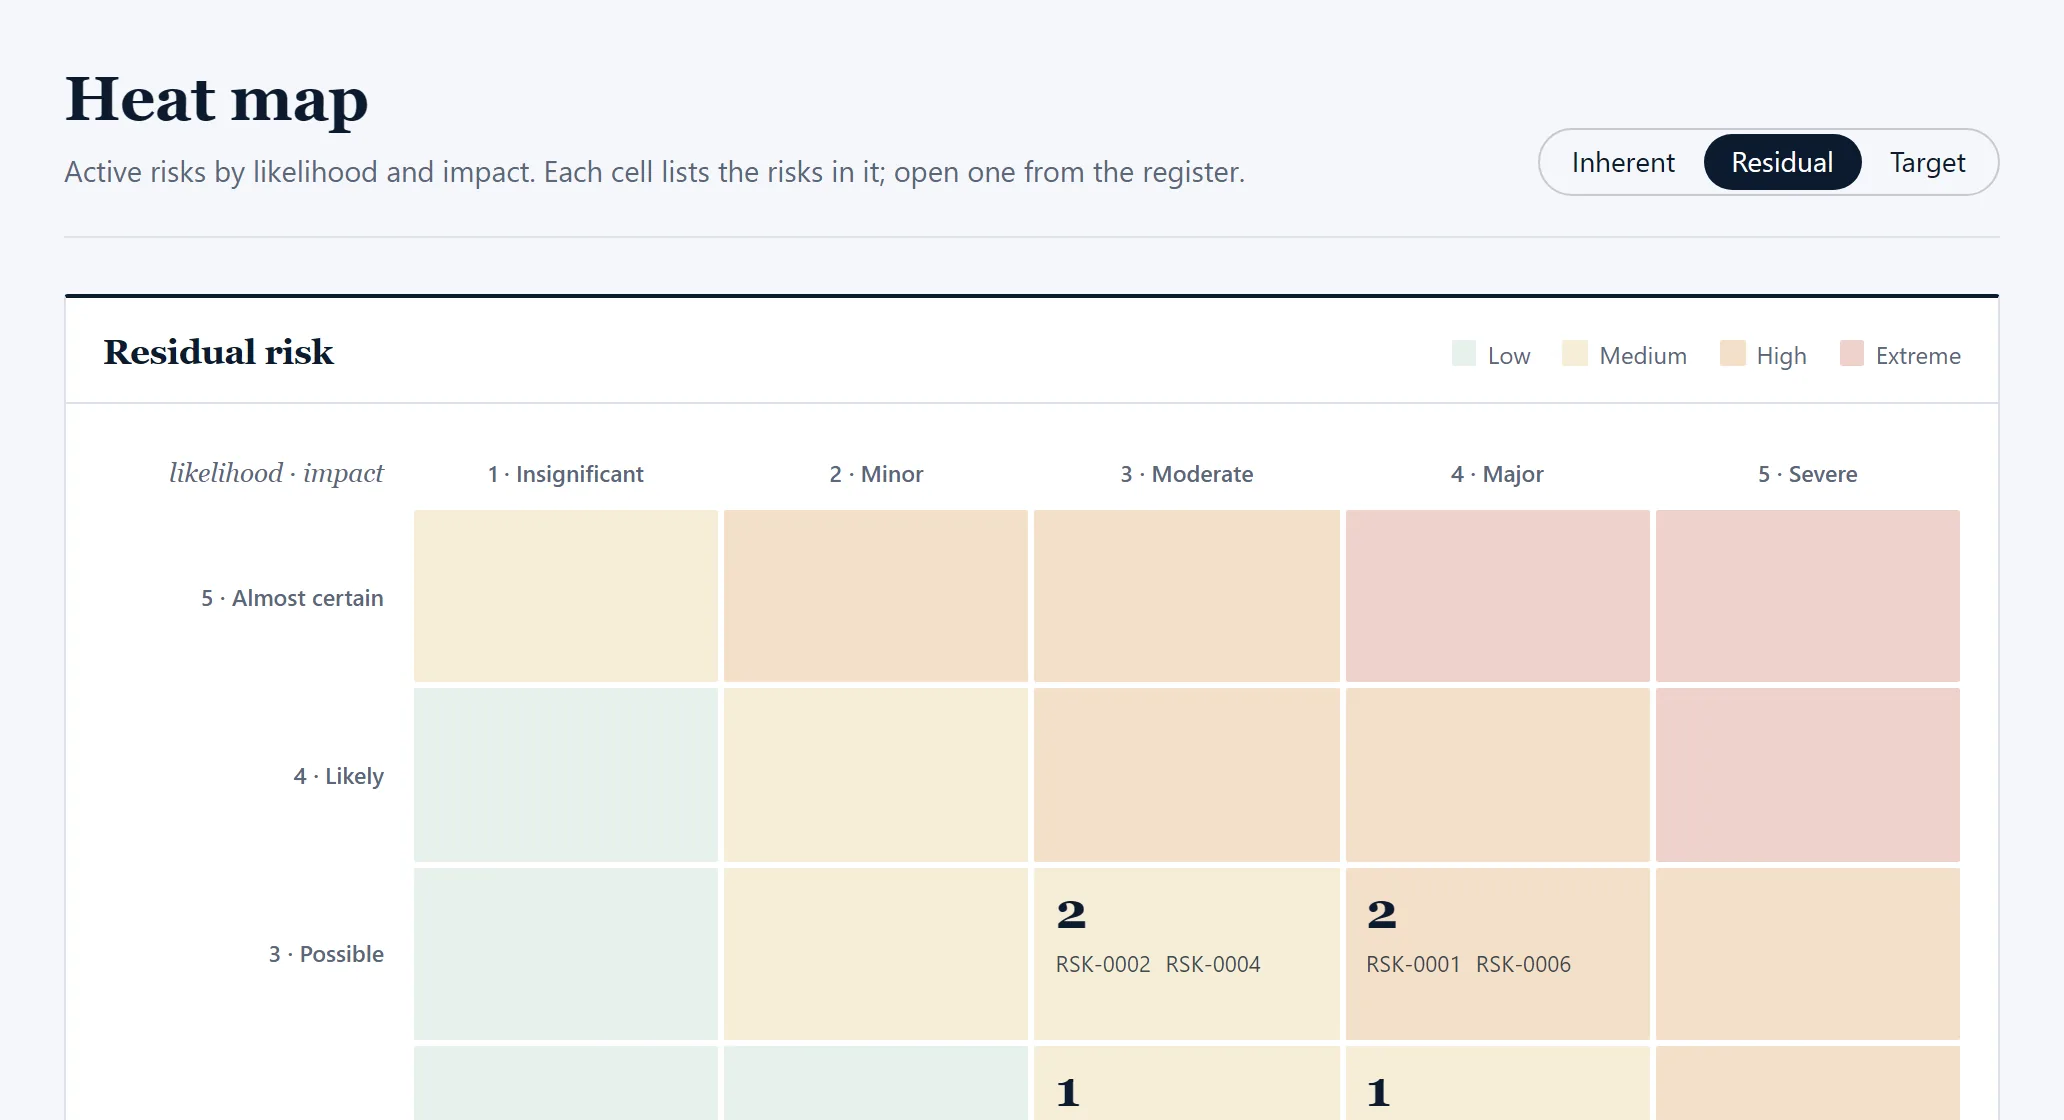
1.1Likelihood and impact on your own matrix: inherent, residual and target scores against the appetite set for each category.
1.2Treatment plans that land in the action register.
1.3Key risk indicators with amber and red thresholds and a history of readings.
1.4One control library with tests and evidence. A failed test raises an action for the control owner.
1.5Mapping to COSO and NamCode, with suggested links for a person to accept or reject.
1.6An incident and loss log shared with compliance.
Compliance
Obligations adopted, not typed
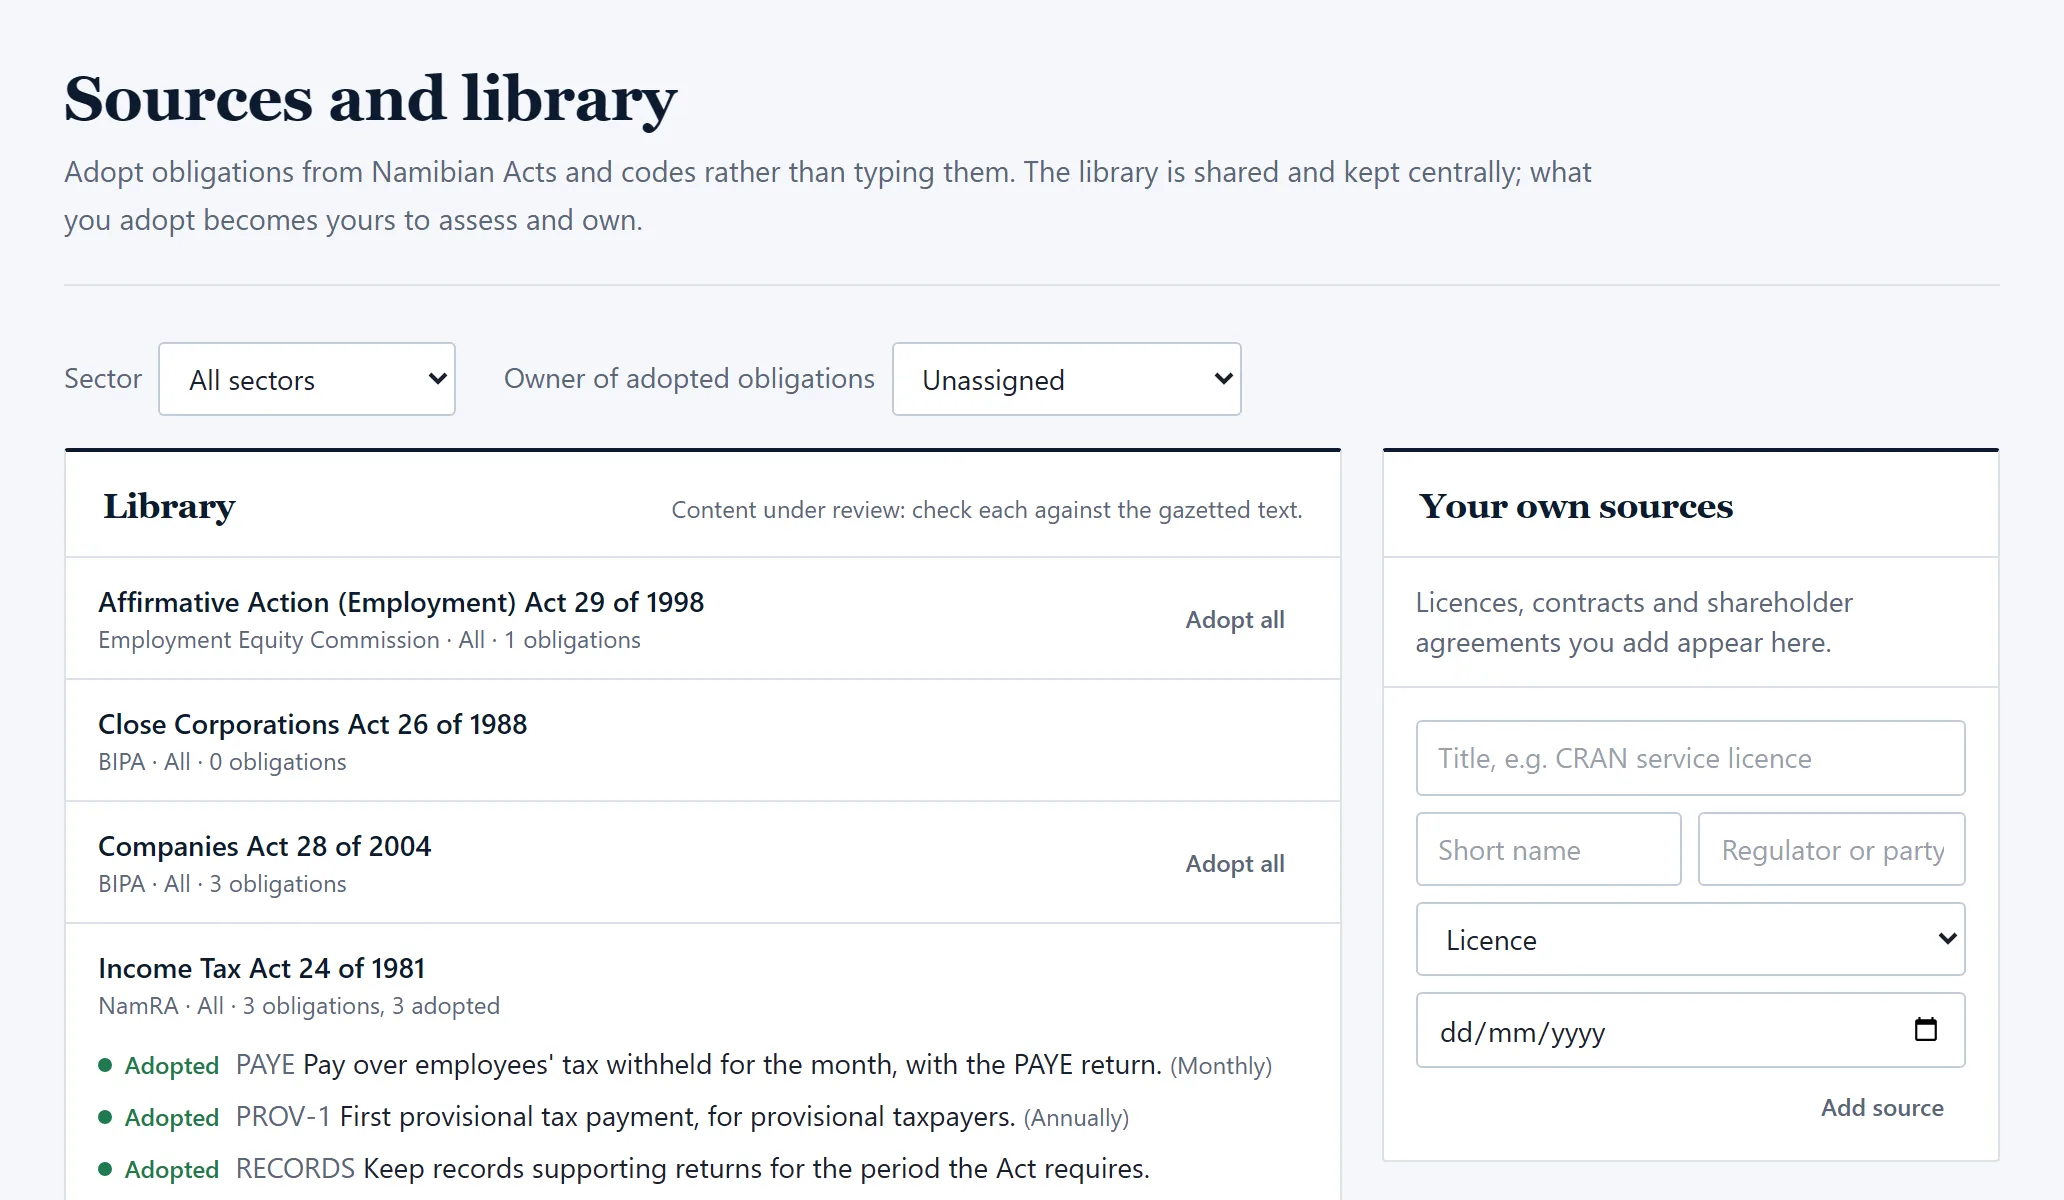
2.1A library of Namibian Acts and codes by sector, alongside your own licences and agreements.
2.2A compliance calendar where a deadline on a weekend or public holiday moves to the business day before.
2.3Assessments that raise an action for every gap, and a breach log.
2.4Policies approved, published and signed for by the people they apply to, with a register of who has not.
2.5Registers of interests and of gifts and hospitality.
2.6Anonymous speak-up, followed up with a case code only the reporter holds.
Internal audit
A file that stands up to review
3.1The audit universe and a risk-based annual plan, taken to the committee for approval.
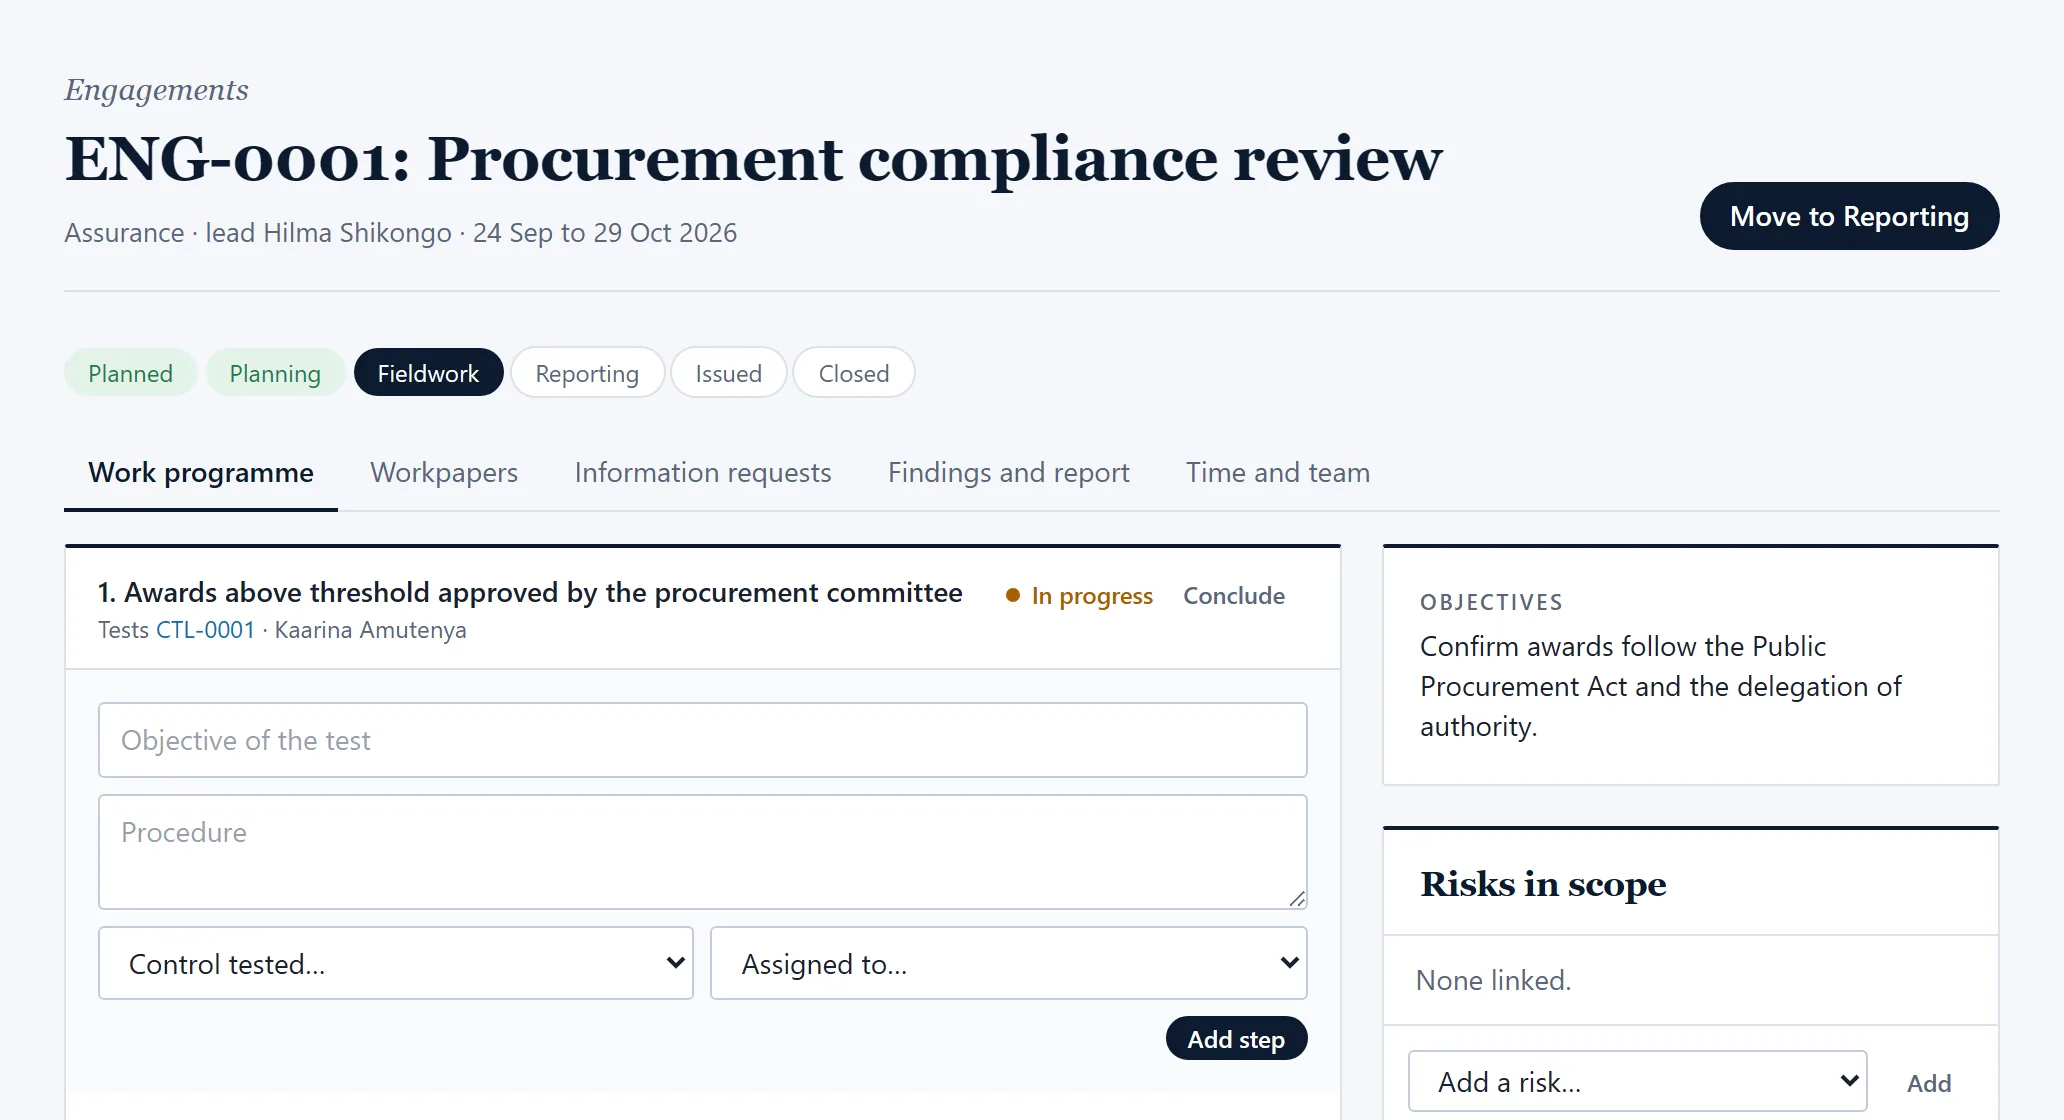
3.2Engagements through planning, fieldwork and reporting.
3.3Information requests to managers, tracked rather than chased by email.
3.4Workpapers signed by a preparer and a different reviewer, with review notes cleared first.
3.5Findings in the standard form, followed up until an auditor has validated every agreed action.
3.6One findings register for internal audit, the external auditor, the Auditor-General and regulators.
Board and committees
From agenda to adopted minutes
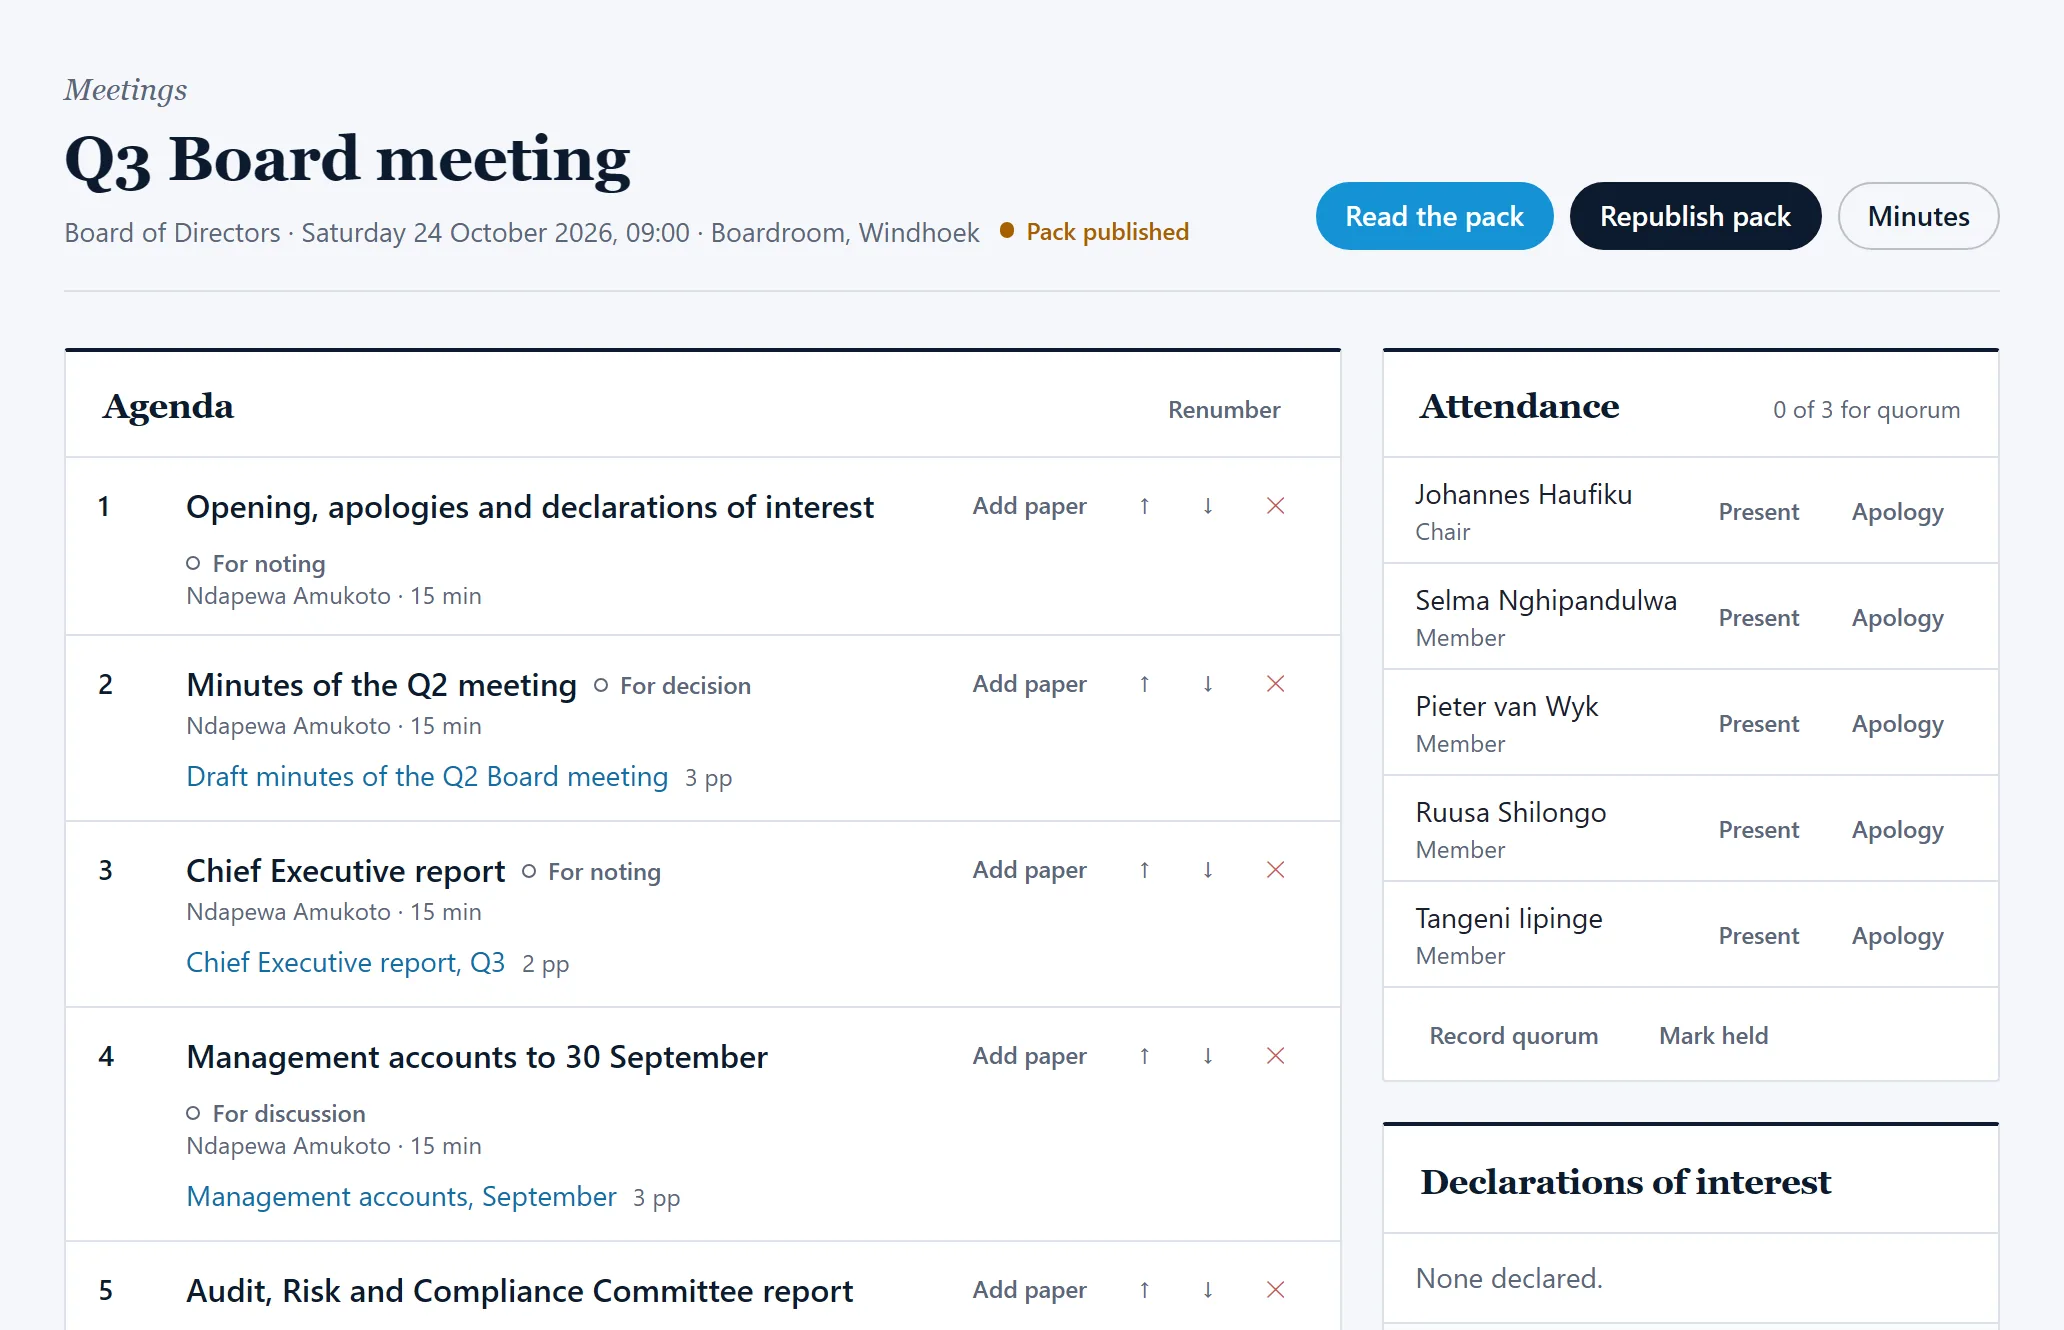
4.1Agendas with the papers behind each item, merged into one pack with a cover, contents and continuous page numbers.
4.2Every director's copy carries their name. Late papers go in as addenda, and the version already read stays as it was.
4.3Private notes on a page that survive the pack being republished.
4.4Minutes drafted from the agenda, circulated for comment, adopted at the next meeting, then locked.
4.5Resolutions in the meeting or by round robin, with quorum, thresholds and recusals, each vote signed against the wording.
4.6Declarations of interest recorded against the item they concern and printed into the minutes.
The committee view
Ready before the meeting
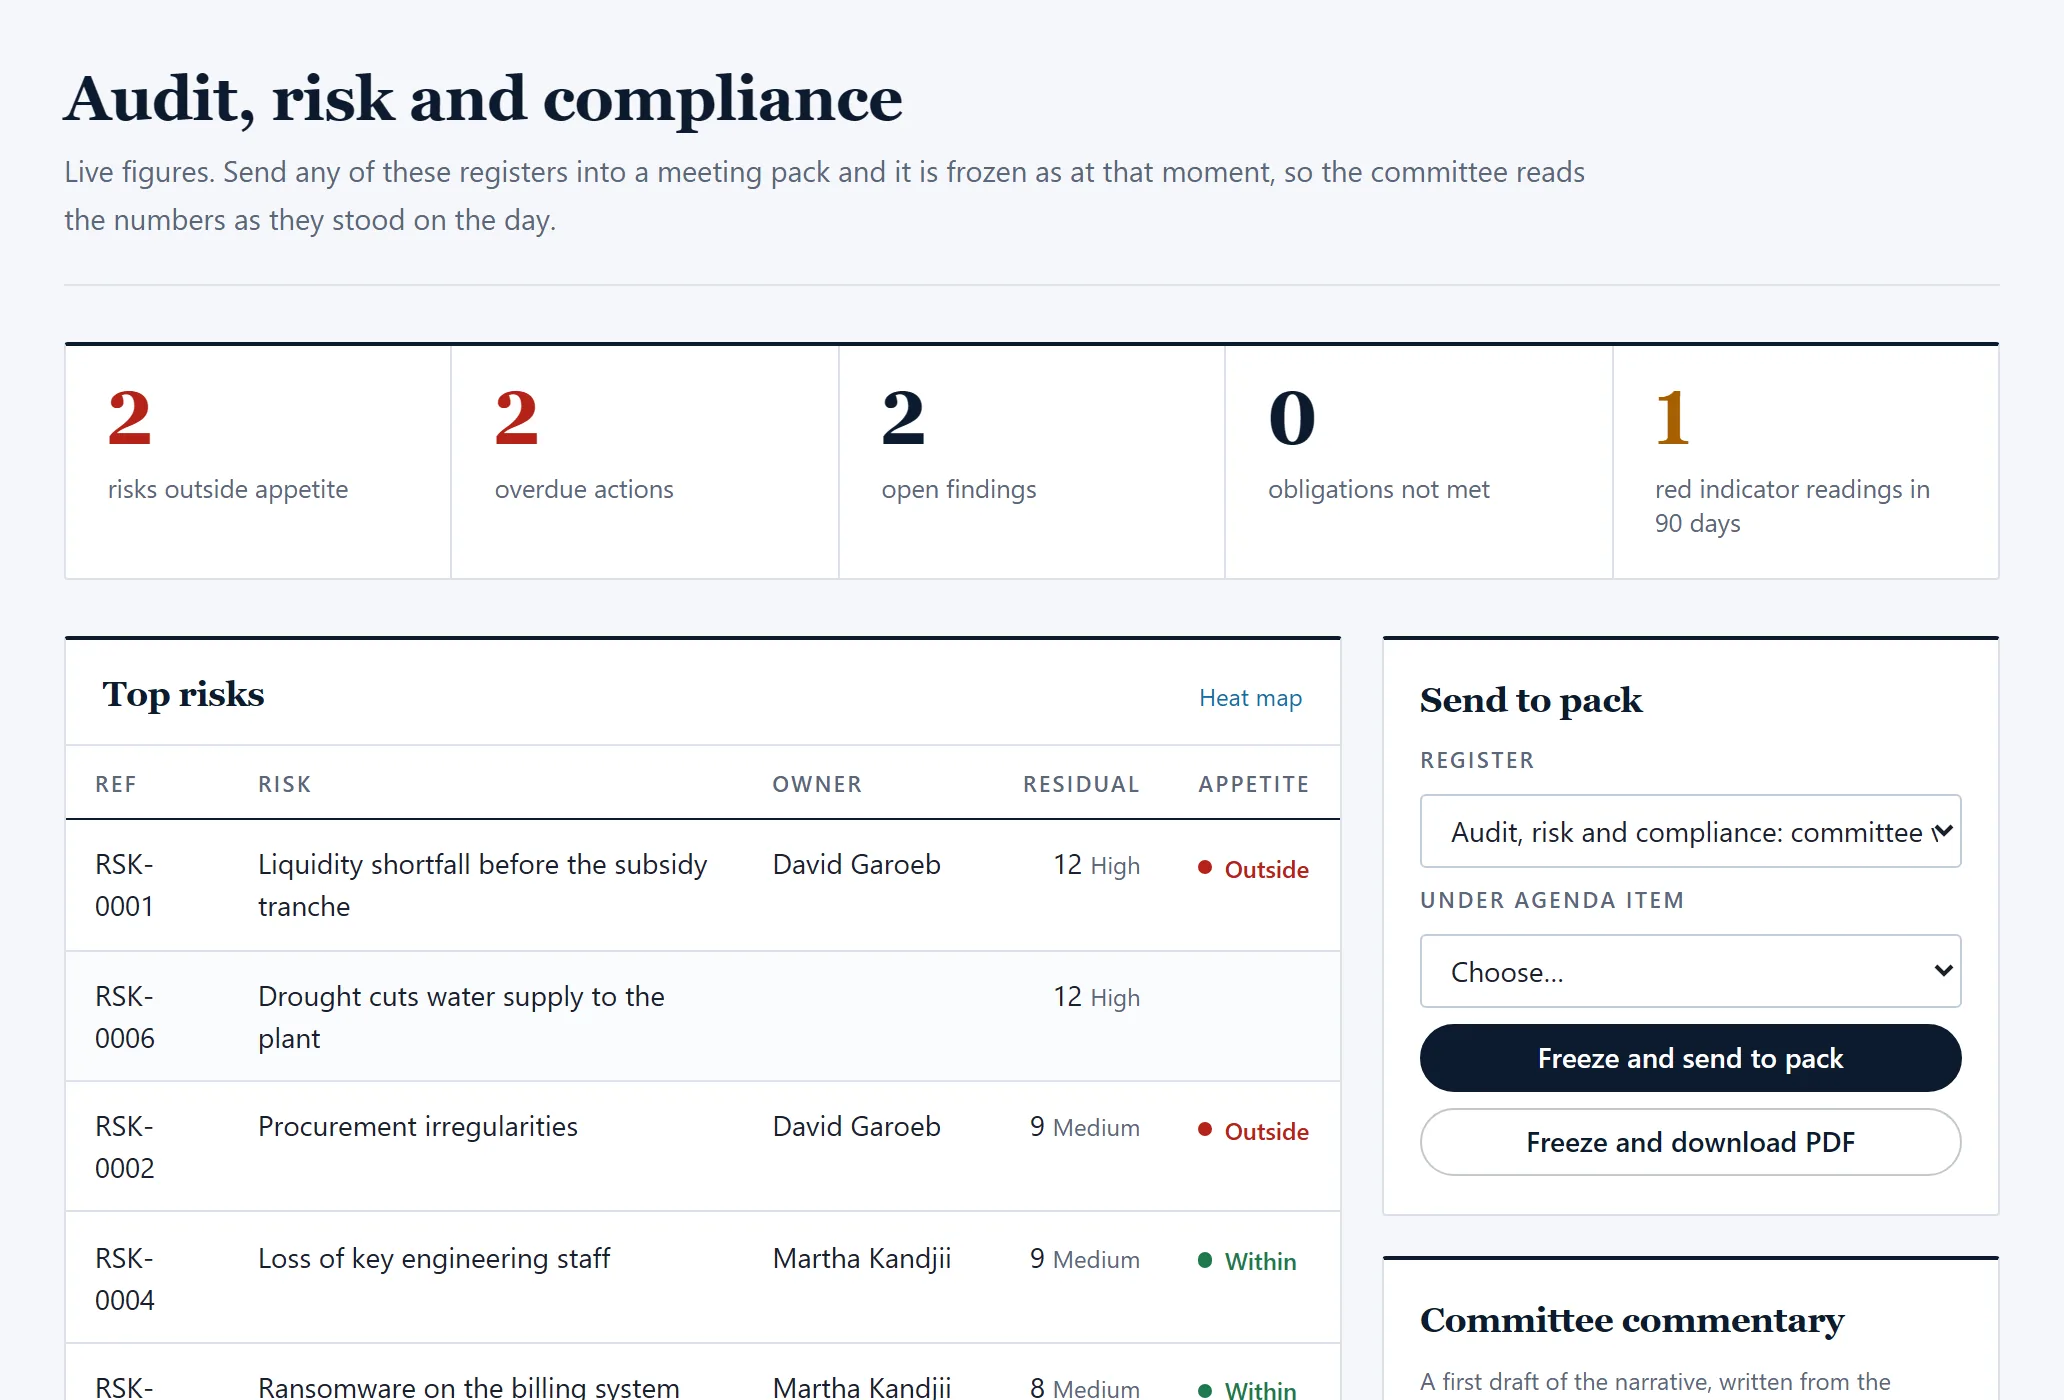
5.1Top risks, overdue actions, open findings by rating and compliance status on one page.
5.2Freeze any register as it stands and it becomes a numbered paper in the next pack.
5.3The committee reads the figures as they were on the day, whatever has moved since.
5.4A first draft of the committee commentary, written from the same figures.
5.5Each person opens the view that concerns them: a director, a risk owner, an auditor.
5.6Every figure leads back to the record it came from.
Built for how Namibian boards work.
Made in Windhoek, around the Acts, codes and certificates Namibian organisations answer to, rather than adapted from somewhere else.
No.
Matter
What GovernCore keeps
1
NamCode, apply or explain
Each part of the Namibian Corporate Governance Code: applied, or the explanation of why not. Reviewed each year and ready to report.
2
Certificates, when you need them
A Social Security good standing certificate runs for about a month. GovernCore tells you when to apply for the tender you are bidding on, not when the last one expires.
3
Public enterprises
Governance and performance agreements with the portfolio Minister, board appointments and terms, and the reporting cycle to the shareholder Ministry.
4
Filings and statutory registers
BIPA annual returns and changes of director, and the Companies Act registers of directors, members and their interests.
5
Procurement oversight
Declarations of interest against a specific procurement, and the committee's record of how the award was decided.
6
Findings from every source
Auditor-General and regulator findings in the same register as internal and external audit, with the same follow-up.
7
Business days
A deadline on a weekend or a Namibian public holiday moves to the business day before.
8
One login, several boards
A director on three boards signs in once and sees each organisation separately, never mixed.
A record that holds up when someone asks who saw what.
Every change, sign-in, opened pack and vote is written to a log that only grows. Each entry is sealed against the one before it, so the history cannot be rewritten without it showing.
Pack version 2 publishedQ3 Board meeting · N. Amukoto · 09:12seal 7f02… after a41c…
Pack openedCopy watermarked for J. Haufiku · 11:40seal c9e8… after 7f02…
Vote cast and signedRES-2026-014 · S. Nghipandulwa · 14:05seal 31bd… after c9e8…
Minutes adopted and lockedQ2 Board meeting · fingerprint kept · 16:30seal e65a… after 31bd…
Separate by design
Every record belongs to one organisation and is only read inside it. Files are encrypted with a key that belongs to your organisation alone.
Named copies
Every pack is watermarked with the name of the person it was issued to, and the system records when each director opened it.
Signatures that mean something
A signature is bound to exactly what was signed. If the wording changes afterwards, the signature shows it.
Minutes that stay adopted
Adopted minutes are locked and fingerprinted, so any later change is visible.
Access by role and by record
A director sees the committees they sit on. A manager answering a finding sees only their own. An external auditor gets access that ends on a date.
Speaking up safely
Reports carry no name, address or device. The reporter follows up with a case code that nobody else can look up.
It drafts. People decide.
GovernCore takes the typing out of governance work without taking the judgement out of it: draft minutes from the agenda and your notes, actions found in a transcript, answers from past minutes with every source shown, and committee commentary written from the registers.
Nothing is sent to an outside AI service. Every use is recorded, and it can be switched off for the organisation or for one committee.
Draft
5. Approval of the 2027 budget
The Chief Financial Officer presented the 2027 budget and business plan. The committee asked how many days of cash cover would remain if the subsidy were paid late, and noted the overdraft facility under negotiation.
Built from the agenda, the attendance, the declarations and the secretary's notes.
N. Amukotoadopted by the Company secretary, 24 Oct, 10:41
Questions boards ask
1Who is GovernCore for?
Boards and their committees, company secretaries, and the risk, compliance and internal audit teams who report to them: companies, public enterprises, financial institutions and associations.
2Can a director who sits on several boards use one login?
Yes. One person signs in once and sees each organisation separately. What they can see in one organisation never shows in another.
3Are our records kept apart from other organisations?
Yes. Every record belongs to one organisation and is only ever read inside it. Files are encrypted with a key that belongs to your organisation alone.
4Does it use AI?
It drafts minutes from the agenda and your notes, finds actions in a transcript, answers questions from your past minutes and resolutions with the sources shown, and drafts committee commentary. Everything it produces is a labelled draft that does nothing until a named person adopts it. Nothing is sent to an outside AI service, and it can be switched off for the organisation or for a single committee.
5Can we start with the board and add risk and audit later?
Yes. The modules share one record, so the board can start with meetings and packs, and the risk register, controls, compliance and audit can follow when you are ready.
See it with your own board in mind.
Tell us about your board and committees. We will take you through a meeting from agenda to adopted minutes, and show the registers behind it.
What happens next
We contact you to agree a time, then show GovernCore on a demonstration organisation set up like yours.